
GAMP 5 Validation.
GAMP 5 is the authoritative ISPE guide to the risk-based validation of computerized systems in GxP environments. Its Second Edition (2nd Edition) was published in July 2022. The new guidance and drafts describe a floodlight, not a flashbulb: ongoing verification in operation, as in PI 006-4, the Annex 15 concept paper and the draft Annex 22. GAMP 5 has that mechanism in its DNA. Change control, periodic review, incident and problem management keep the validated state across the whole life cycle. As part of the 2nd Edition Core Team, we apply this life cycle principle to CSV as well as to equipment qualification and process validation.
The reference for computerized systems.
The GAMP 5 Guide offers a pragmatic framework for efficiently delivering compliant computerized systems that are fit for their Intended Use. Its risk-based approach, grounded in scalable specification and verification, has proven effective for systems of all sizes.
What is new in the GAMP 5 2nd Edition?
The GAMP 5 2nd Edition (July 2022) retains the framework, the key concepts and the quality risk management aligned with ICH Q9. The guidance on applying it in practice has been updated, and the emphasis has shifted: patient safety and product quality come before compliance, and critical thinking is called out explicitly. The 2nd Edition also stresses more strongly than the First Edition that the life cycle need not be linear, with a dedicated appendix on iterative and agile development. New appendices cover critical thinking, in-house and third-party IT infrastructure, software tools across the life cycle, blockchain, plus AI and machine learning. The 2nd Edition has also reworked planning and reporting for SaaS solutions, the assessment of cloud service providers, requirements and testing with tool support, and the handover into operation. The guide allows records from automated tools to replace formal specification and test documentation. In doing so it applies the Computer Software Assurance concepts from the FDA's Case for Quality program.
How does a GAMP 5 validation work?
A GAMP 5 validation follows the guide's life cycle model with four phases: concept, project through to go-live, operation and retirement. The preparatory work takes place in the concept phase, so that the context stops shifting during the project and no tasks from earlier phases have to be finished during the project. The project phase covers planning, specification, configuration or development, verification and release, with scope and depth scaled to risk, complexity and novelty. In operation, change control, incident and problem management, configuration management and periodic review maintain the validated state. The GAMP 5 2nd Edition calls for critical thinking along the way. In the end, the evidence must show that the system is fit for its Intended Use and can be operated in a validated state.
| Phase | What happens |
|---|---|
| Concept | The business derives need and Intended Use from its process; an initial risk assessment and the in-principle decision on the solution approach and the supplier. |
| Project | Planning, specification, configuration or development, verification and release are scaled according to risk; supplier deliverables are assessed and leveraged rather than duplicated. |
| Operation | The longest phase: change control and configuration management, periodic review, and incident and CAPA processes maintain the validated state. |
| Retirement | An orderly exit: data migration or archiving in line with retention requirements. The records remain readable and available beyond the life of the system. |
The V-model describes specification and verification: it pairs each level of specification with its matching verification. It covers exactly one phase, the project; concept, operation and retirement do not appear in it. The V-model sits inside the life cycle, but it is not the life cycle. The guide itself drew that conclusion early. The First Edition (2008) had already moved away from the classic V diagram because the V had too often been misread as a linear waterfall. The 2nd Edition carries the generic representation of specification and verification forward. The same logic applies to iterative, agile approaches, where it is worked through in increments.
What the system produces follows IT's oldest pattern: input, processing, output. A function turns input data into results; the sum of the functions is the system. Its outputs are electronic records and signatures. They are subject to 21 CFR Part 11 and Annex 11, and the evidence that they are generated in compliance is produced as part of validating the system. Annex 11 is part of the GMP framework. The principle applies across the entire GxP spectrum. In clinical research, for instance, it is set out in ICH E6(R3) and the EMA guideline on computerised systems.
What goes into a GAMP 5 validation?
A GAMP 5 validation consists of a chain of evidence. It begins in the concept phase and closes the project with the validation report. Each link answers a question an inspector will ask later, such as what the system is meant for, which risks were identified, how it was tested and who released it. Eight steps deliver the core of that evidence. How deep each step goes is set by the risk. The chain does not end with release. Every later change to the system runs through it again, scaled to the size of the change. The periodic review establishes whether the evidence still matches the system in use. Keeping the evidence current in operation maintains the validated state that GAMP 5 describes as the goal of the operational phase.
The risk process behind the evidence.
Within the phases, quality risk management governs what evidence is produced and how deep it goes. ICH Q9 describes the systematic process. GAMP 5 translates it into five steps for computerized systems:
- 1
Initial risk assessment
A first appraisal of the system in its process context: How does it influence GxP-relevant operations? What is the system's overall impact level?
- 2
Identify the relevant functions
Which functions touch patient safety, product quality or data integrity? The depth of testing follows the risk of these functions.
- 3
Functional risk assessment & controls
For each of these functions, failure scenarios are identified and assessed. From that assessment the validation team derives technical, procedural or organizational controls.
- 4
Implement & verify controls
The controls are implemented and verified in a documented way, traceable back to the requirement they safeguard.
- 5
Review periodically
Risks and controls are reassessed regularly in operation and adjusted where needed.
Software categories: a continuum, not a checklist.
The GAMP categories classify software by type and degree of customization. Two causal drivers underlie them: novelty and complexity. The more customization a regulated company demands, the further it moves away from the standard product. The supplier's assessable deliverables then cover less of the required evidence, and the company's own share grows accordingly.
| Category | What follows from it |
|---|---|
| 1 · Infrastructure softwareoperating systems, databases, middleware | Established and widely deployed, hence low novelty. Infrastructure is kept under control and qualified. The guide does not call for validating the individual components. |
| 3 · Standard productsnon-configured, used "as supplied" | The evidence rests on the supplier's assessed deliverables and on the company's own verification against its requirements. |
| 4 · Configured productsLIMS, MES, eQMS, ERP | The configuration is the new, unproven part. The evidence concentrates on the configuration and on the processes it maps. |
| 5 · Custom applicationsbespoke development, custom code | With maximum novelty there is no assessable prior work. The complete evidence from specification to testing rests with the regulated company, supported by its supplier. |
The 2nd Edition makes clear that the categories form a continuum. Real systems mix components from several categories. An MES, for instance, contains parts of categories 3, 4 and 5 at once. And the category is only one scaling factor alongside GxP impact, complexity and novelty. Anyone who reads the category as a validation checklist misses the risk. How widely a product is deployed plays its own role: the more users a standard function has, the greater the supplier's own interest in keeping that standard free of defects. A defect there immediately damages the supplier's reputation. Yet only what the supplier presents as assessable deliverables feeds into the evidence. Applied correctly, GAMP 5 makes validation efficient: the requirements are written to be verifiable, the decisions are justified by risk, and the supplier's deliverables, targeted tests and tools are put to use. The effort lands where the risk is.
Frequently asked questions about GAMP 5 validation.
No. EU GMP Annex 11 requires validation expressly. 21 CFR Part 11 presupposes a validated system so that electronic records and signatures can be trusted. GAMP 5 is not a regulation. The guide describes how the industry produces that evidence on a risk basis. The FDA's CSA guidance, in its current revision (02/2026), names the 2nd Edition as one source of information on testing methods.
Risk-based. Alongside scripted testing, the 2nd Edition explicitly encourages exploratory and unscripted testing as well as test automation. Electronic records from tools may take the place of formal test documents. The measure is demonstrable coverage of the risk-relevant requirements, whatever template is used.
Yes, explicitly since the 2nd Edition. It takes medical device regulation into account and addresses manufacturers' production and QMS systems. The First Edition still excluded software embedded in medical devices.
No. Computer Software Assurance is how the FDA gives concrete form to risk-based testing for the production and QMS software of medical device manufacturers. The two documents refer to each other in passing, without positioning themselves against each other. The CSA guidance names GAMP 5 once in a footnote on testing methods, and GAMP 5 in turn refers to the FDA's earlier CSA work in its chapter on testing and in its glossary. GAMP 5 provides the life cycle and CSA sharpens the test strategy, both for the same evidence.
The regulated company. It can involve suppliers and service providers and use their evidence, provided it has assessed that evidence. Responsibility for the validated state stays with the operator, even when third parties deliver the work. GAMP 5 describes the roles of process owner and system owner for this. The business owns Intended Use and requirements, IT owns operation and the quality unit owns the independent review.
QFINITY on the GAMP 5 2nd Edition Core Team.
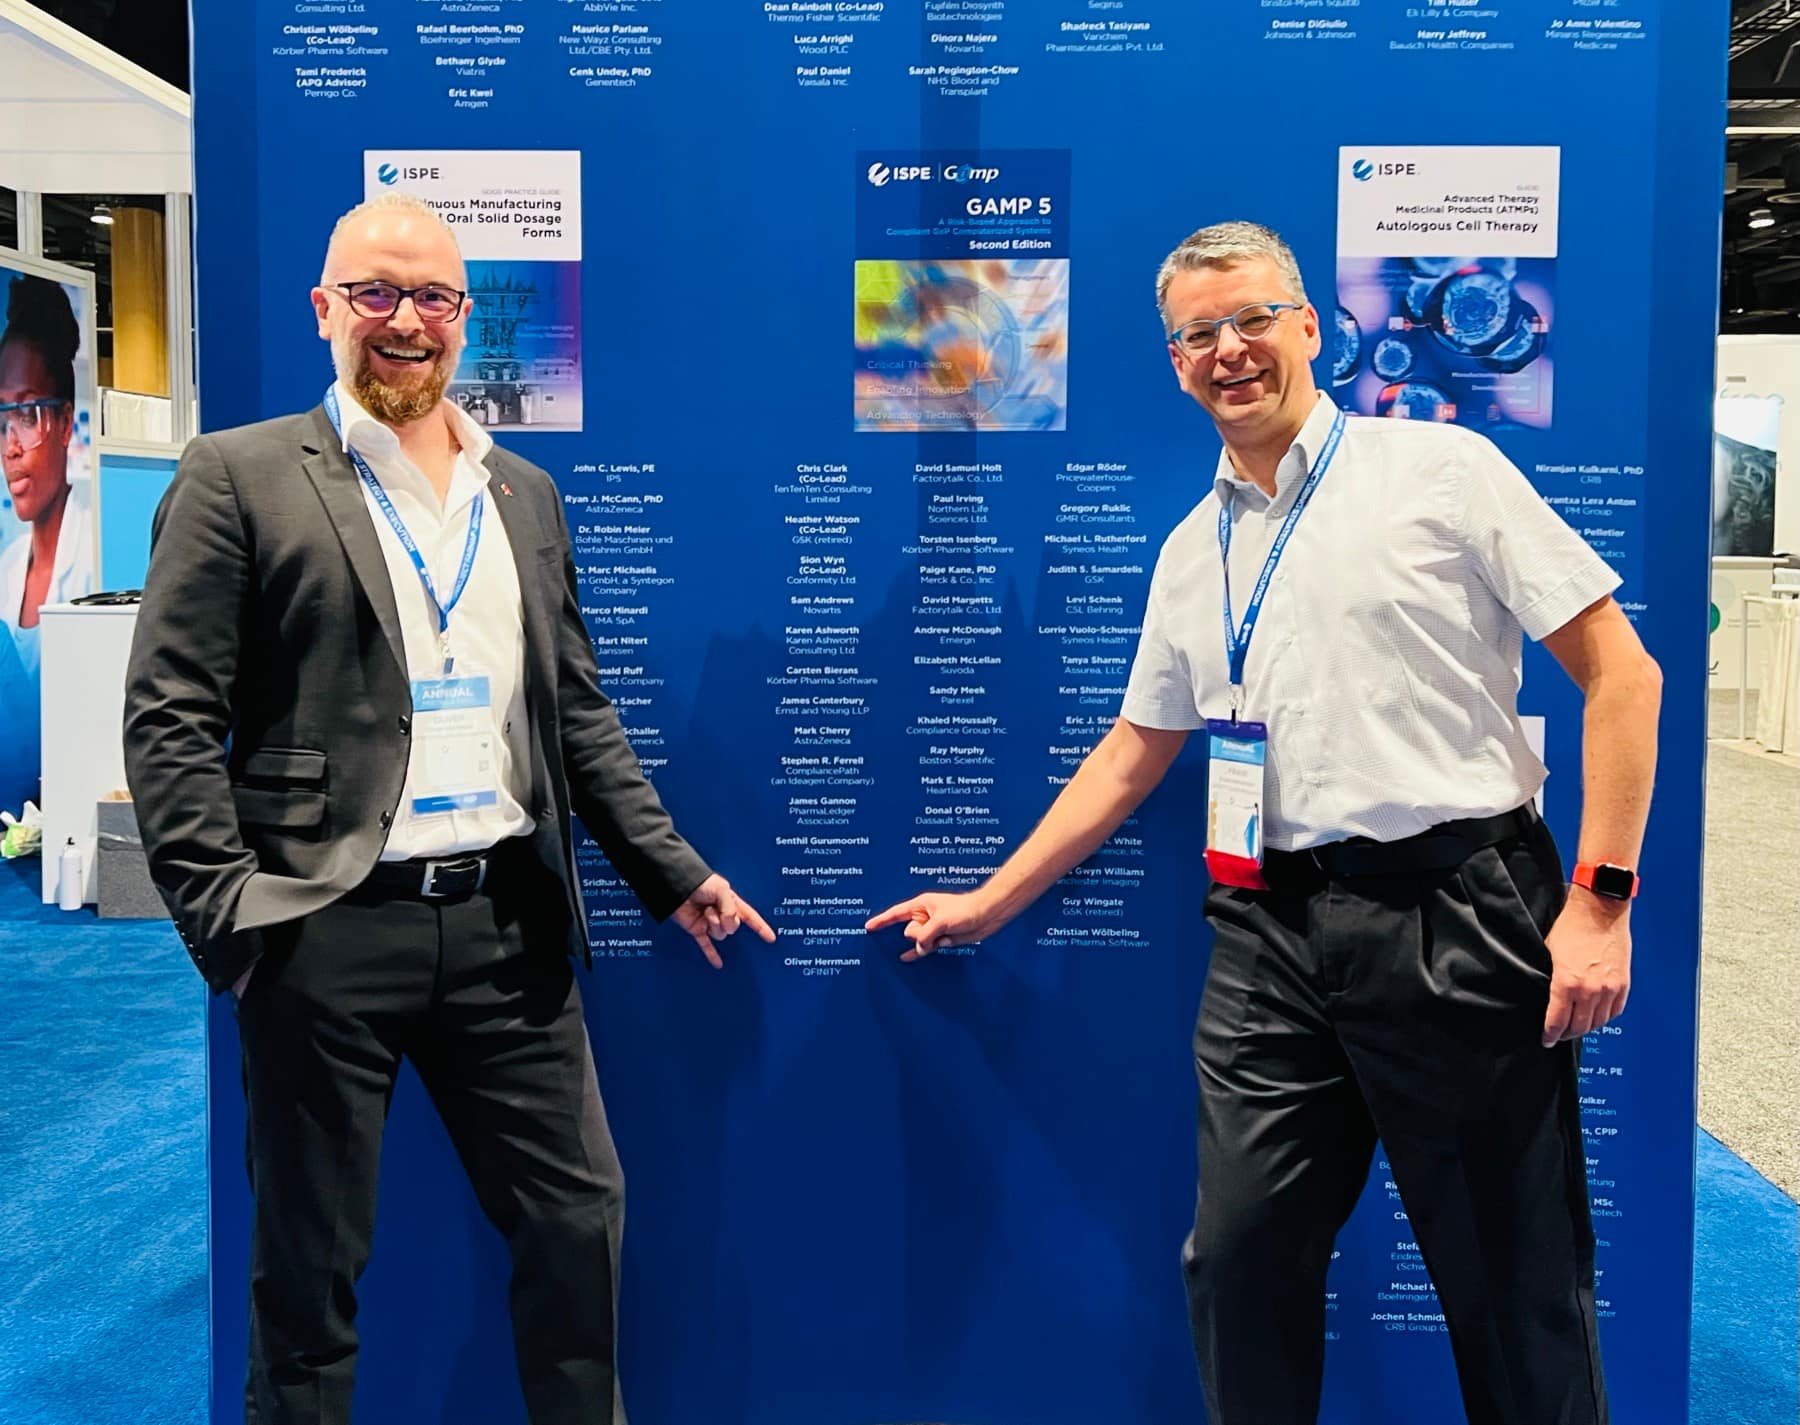
As a long-standing, active member of the ISPE GAMP Community, QFINITY worked on the Core Team, contributing to the creation and review of the guide. That experience counts wherever the text leaves room for judgment: we know the intent behind the wording. The Core Team also included members of the FDA Industry CSA team (FICSA), so the CSA perspective fed straight into the 2nd Edition. The GAMP Good Practice Guide "Testing GxP Systems" (3rd Edition, July 2026) shows how closely the two strands are interwoven. FICSA members contributed to it, and Frank Henrichmann (QFINITY) reviewed it for the ISPE Editorial Review Board. A dedicated chapter covers computerized test tools and assesses them according to ISPE GAMP 5 (2nd Edition). Our assessment of the 2nd Edition appeared as an article in Pharm. Ind. The S/4HANA conversion case study shows how the methodology proves itself in an engagement: validated, and taken live without local outages.
- Contributed to the creation and review of GAMP 5 2nd Edition
- Frank Henrichmann: Chair of the GAMP Global Steering Committee
- Oliver Herrmann: GAMP Track Lead, ISPE Europe Annual Conference 2026
- Qualified ISPE GAMP trainers
- Contributed to the GPG "Enabling Innovation", which the 2nd Edition builds on
The guide the FDA itself points to.
QFINITY presented the 2nd Edition just months after its release, at the 15th official GAMP 5 conference in Mannheim (2022). The FDA itself has long drawn on the guide as a reference. In 2003 its Part 11 guidance cited the GAMP 4 Guide for validation, and since its 02/2026 revision the CSA guidance has named the 2nd Edition for testing methods. Neither the draft nor the original final version contained that reference.
Last updated:
From the guide to everyday practice.
Let's talk about your validation.
We translate GAMP 5 2nd Edition into a concrete validation strategy for you, from risk-based CSV and Computer Software Assurance to AI/ML, agile and cloud/SaaS. Your first consultation is free, takes about 30 minutes, and puts you directly in touch with a Core Team contributor. You name the system and its category; we tell you what evidence we consider appropriate for it, and what you can do without.
Book an intro call
